Bitcoin exchanges can reduce quantum exposure before a network upgrade
A future quantum-safe Bitcoin will have to pass through the systems that hold and move today's coins. Exchanges, institutional custodians, hardware wallets and key-management platforms would all need to adopt new rules while continuing to process deposits, withdrawals, approvals, backups and recoveries.
That operational challenge moved to the center of the debate after Coinbase published a September 9 account of a post-quantum Bitcoin workshop it hosted with Stanford and Localhost Research. Coinbase said the closed-door session brought together developers, cryptographers, institutional custodians and hardware-wallet experts. Participants reached no consensus on an exact post-quantum approach and identified open tradeoffs involving transaction size, hardware performance, key management and adoption.
An earlier Glassnode exposure study gives that rollout problem a measurable scale. Its May data placed roughly 1.6 million BTC in exchange-related outputs whose public keys were already visible on-chain.
A visible public key is not a present theft condition. Sources published through September described no cryptographically relevant quantum computer capable of breaking Bitcoin's signatures, and Coinbase called the risk non-immediate. The measurement instead identifies coins that a sufficiently capable future machine could target without waiting for their owners to spend.
A 1.6 million BTC custody cohort
Bitcoin signatures allow the network to verify that a spender controls a private key. Conventional computers cannot feasibly derive that private key from its public counterpart. Shor's algorithm running on a sufficiently capable quantum computer could, in principle, break that assumption.
Public-key visibility therefore divides the risk into two time windows. An at-rest, or long-exposure, attack would target a key that has remained visible on-chain. A short-exposure attack would target a key revealed only after a transaction enters the mempool, giving an attacker a brief window before confirmation.
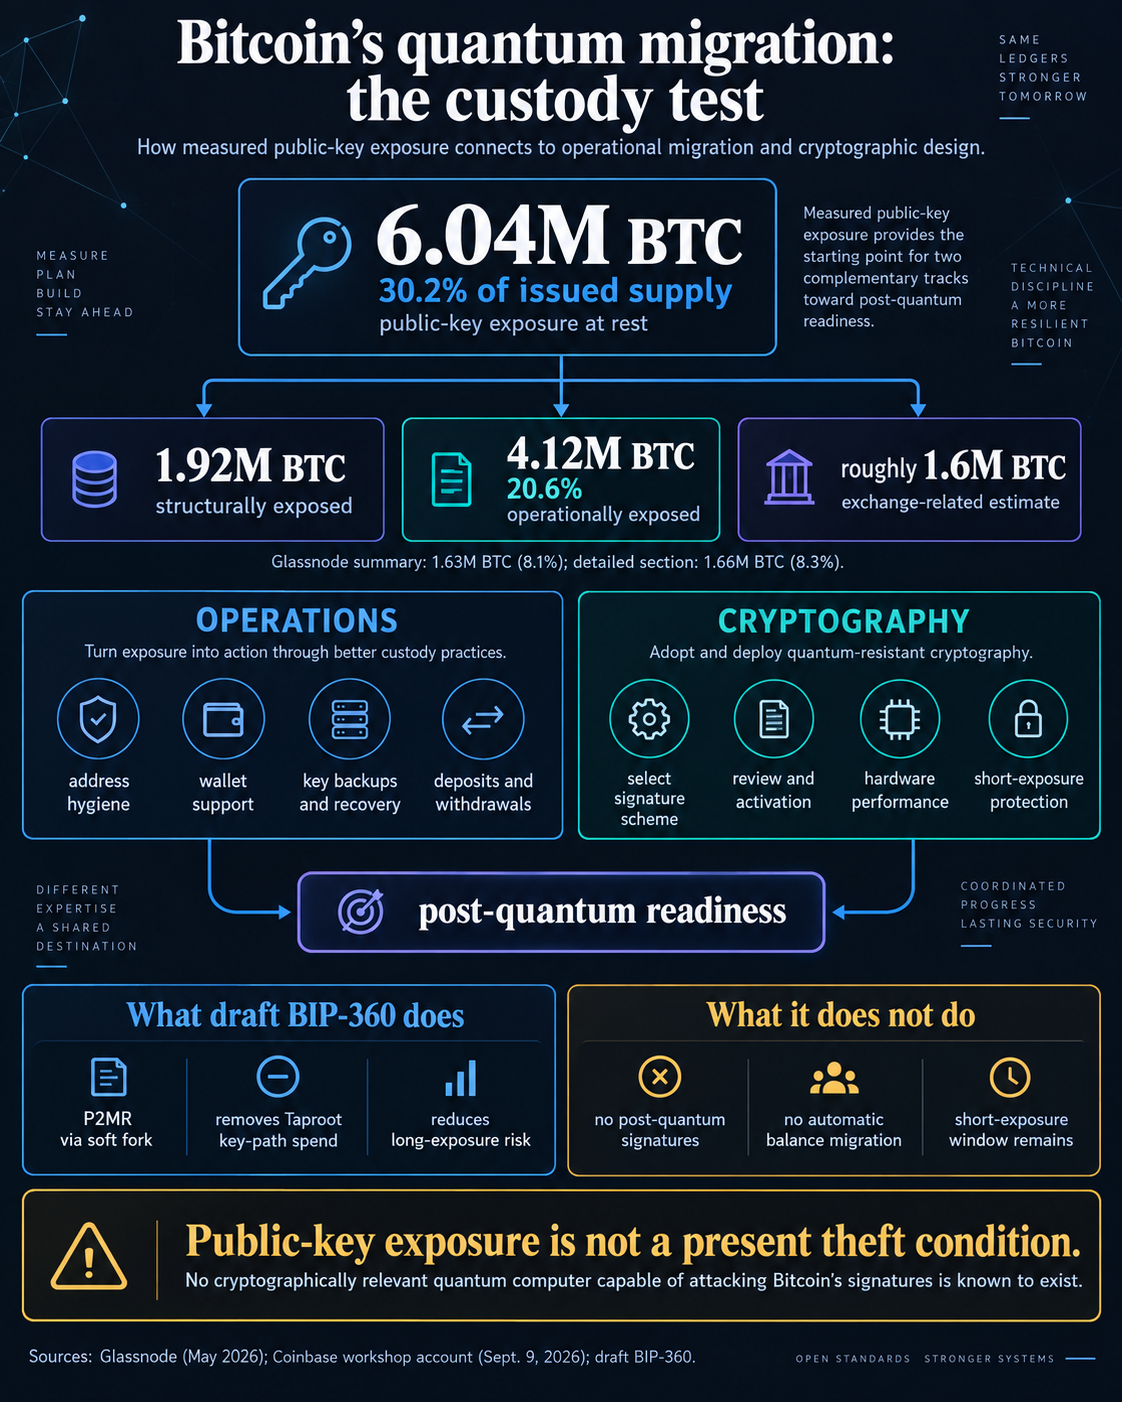
Glassnode estimated that 6.04 million BTC, or 30.2% of issued supply, had public-key exposure at rest in May. The firm classified 1.92 million BTC as structurally exposed because the output type reveals a key or equivalent by design. It attributed 4.12 million BTC, or 20.6%, to operational behavior such as address reuse or leaving a balance associated with a key after a spend revealed it.
Exchange-related balances were the largest labeled part of that operational bucket. Glassnode's summary gives 1.63 million BTC, or 8.1% of supply, while its detailed section gives 1.66 million BTC, or 8.3%. Those two slices support a shared description of roughly 1.6 million BTC, equal to about 40% of the study's operationally exposed total.
The label has limits. Glassnode presented exchanges as an attributed subset of on-chain balances rather than an exhaustive inventory, and it cautioned against reading the data as a security, solvency or immediate-risk ranking. The results also varied widely: Coinbase-attributed balances showed 5% exposure under the methodology, while several peers showed much higher shares. Custody scale alone did not determine exposure.
Active control gives exchanges tools that dormant holders lack. Glassnode said address hygiene, change-output rotation and reserve management could shrink operational exposure before Bitcoin adopts a post-quantum signature scheme. A custodian still has to coordinate policies, approvals, backups, deposit addresses and withdrawals, yet it can decide to move a controlled balance.
Dormant and lost-key coins sit at the opposite end of that spectrum. A March Google Quantum AI paper separated active holdings that can migrate from abandoned or inaccessible assets whose owners cannot produce a valid transaction. Protocol changes can create a safer destination, but they cannot make an absent keyholder sign.
That distinction turns the exchange pool into a large test of execution rather than a verdict on the hardest part of migration.
| Workstream | Current evidence | Remaining work |
|---|---|---|
| Long-exposure reduction | Address hygiene can reduce operational exposure | Move existing balances and deploy safer output types |
| Short-exposure protection | Candidate post-quantum signatures are being studied | Choose, integrate and activate a scheme |
| Custody deployment | Device benchmarks and an MPC simulation show bounded feasibility | Validate production controls, backups and interoperability |
| Dormant holdings | Exposure can be measured | Resolve assets that cannot voluntarily migrate |
BIP-360 opens a path while operations catch up
BIP-360 separates long-exposure mitigation from the choice of a post-quantum signature. The draft Bitcoin Improvement Proposal would add Pay-to-Merkle-Root, or P2MR, as a new SegWit output through a soft fork.
P2MR keeps Taproot-style script-tree functionality and removes Taproot's key-path spend. Funds could be committed to a script tree without leaving a public key visible in the output by default, reducing the attack surface for long-exposure attacks.
The draft adds no post-quantum signature algorithm. Existing exchange balances, legacy outputs and current Taproot coins would remain where they are until their controllers moved them. P2MR also leaves the short-exposure window open because spending generally reveals a public key while a transaction awaits confirmation. BIP-360 says a separate post-quantum signature proposal may be needed for that window.
Activation would therefore create an optional destination, followed by the operational work of adding wallet support and moving balances. The proposal's draft status also matters: it has no activation timeline and represents one approach under review.
Recent experiments have started to narrow individual deployment questions. On August 19, Blockstream Research published benchmarks showing that several tested hardware wallets could generate the hash-based post-quantum signatures used in its study. Its scope covered signature generation on those devices and excluded post-quantum firmware verification, lattice-based schemes and isogenies.
The result demonstrates bounded device capability. Manufacturers would still need to select supported algorithms, secure firmware and backups, build recovery paths and integrate with whatever rules Bitcoin ultimately adopts.
Institutional custody has reached a similarly early testing stage. BitGo, a regulated custodian, and MPC security firm Silence Laboratories reported a post-quantum transaction simulation in May using ML-DSA inside a multi-party computation wallet workflow. The exercise covered distributed key control, policy enforcement and separation of duties. Its status as a simulation leaves production deployment across Bitcoin exchanges unproven.
These tests break a broad migration into specific engineering questions. A device's ability to produce a signature, a custody platform's ability to enforce policy and Bitcoin's ability to verify a new algorithm are distinct layers. Each layer can succeed in isolation while the combined migration remains incomplete.
Two tracks define readiness
Coinbase's workshop account puts cryptographic design and operational rollout on parallel tracks. Signature families carry different costs in transaction size, hardware performance, security assumptions and key management. Deployment then has to carry the chosen design across institutions and individuals without interrupting access to funds.
The available evidence does not rank one track above the other. Exchanges concentrate a large, actively managed exposure and may be easier to coordinate than dormant holders. Their complexity also makes them a demanding test of safe execution. A cryptographically elegant proposal would achieve little if custodians and wallets could not deploy it; flawless operations would have no destination until Bitcoin agreed on new protocol rules.
Near-term progress can be measured without attaching a date to a quantum threat. Custodians can reduce reuse, map exposed balances and test changes to key generation, backups, approvals, deposits and withdrawals. Hardware makers can benchmark candidate schemes and firmware paths. Developers can evaluate P2MR alongside signature proposals that cover the short-exposure window.
The roughly 1.6 million BTC identified by Glassnode is valuable because it turns an abstract transition into a visible cohort. Its active operators have both the ability to act and the burden of proving that large-scale migration can work. Success there would address one material slice of Bitcoin's exposure. Dormant coins, ecosystem consensus and the final cryptographic choice would still remain.
The post Bitcoin exchanges can reduce quantum exposure before a network upgrade appeared first on CryptoSlate.