Core Lightning patches critical security flaws and a Bitcoin payment bug
Core Lightning, software for running Bitcoin Lightning payment nodes, has released v26.06.9 with security fixes and a repair for a regression that could delay channel traffic on busy nodes running v26.06.8.
GitHub lists the new release as published Oct. 7, while its versioned changelog carries an Oct. 6 date.
The update gives operators who installed v26.06.8 a fresh decision on upgrading, following the Sept. 27 revoked-channel penalty flaw that was fixed in v26.06.7. The latest patch adds fixes and addresses a regression introduced by that later version.
Bitcoin payment delays and shutdown risk
In v26.06.8, routine gossip, pings, and onion messages counted toward a CPU budget intended for gossip queries. On busy nodes, that accounting could throttle peers and delay channel traffic, according to the maintainers.
V26.06.9 reserves that budget for gossip queries, so ordinary messages no longer consume it, removing the documented cause of this throttling. The regression described by maintainers concerns busy nodes running Core Lightning v26.06.8.
The changelog also describes a fix for a payment contract (HTLC) that reaches its deadline while a channel is shutting down. V26.06.9 now force-closes the channel in that situation, preventing forwarded funds from being lost if the payment is fulfilled late.
For an operator forwarding payments, this fixes a funds-protection problem when payment deadlines and channel shutdown overlap.
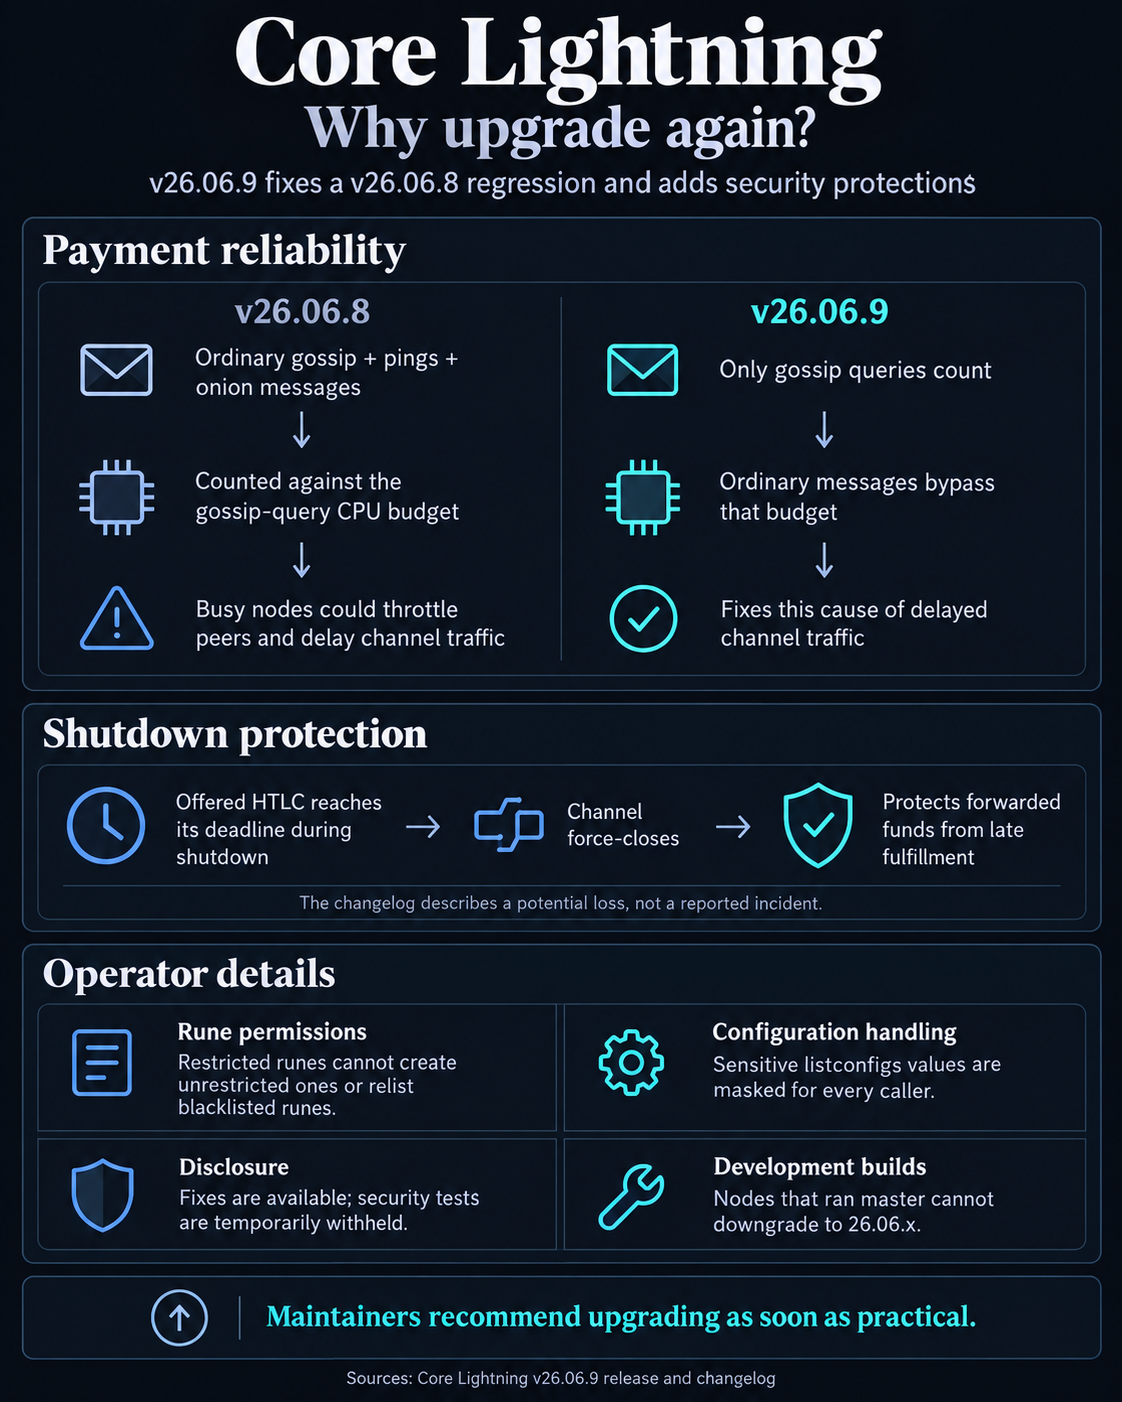
Other fixes enforce the limits carried by runes used to authorize calls, so a restricted rune can no longer create an unrestricted one or relist blacklisted runes. Restrictions on the corresponding creation and blocklisting methods now also cover the invokerune and destroyrune aliases.
The listconfigs command now masks several sensitive values, including recovery information and Bitcoin RPC passwords, for every caller. The setconfig command closes a path for injecting configuration lines through persistent option values.
The fixes are available immediately, but maintainers have temporarily held back security tests to make exploit development harder and give operators more time to upgrade.
Nodes that have run master cannot downgrade to a 26.06.x release because their database schema is newer. The release also reiterates that dual funding remains experimental and discourages zero-confirmation channels with untrusted peers.
Maintainers urge Core Lightning users, including those on v26.06.8, to upgrade to v26.06.9 as soon as practical.
The post Core Lightning patches critical security flaws and a Bitcoin payment bug appeared first on CryptoSlate.