EU regulators target non-compliant stablecoins with a 90-day deadline
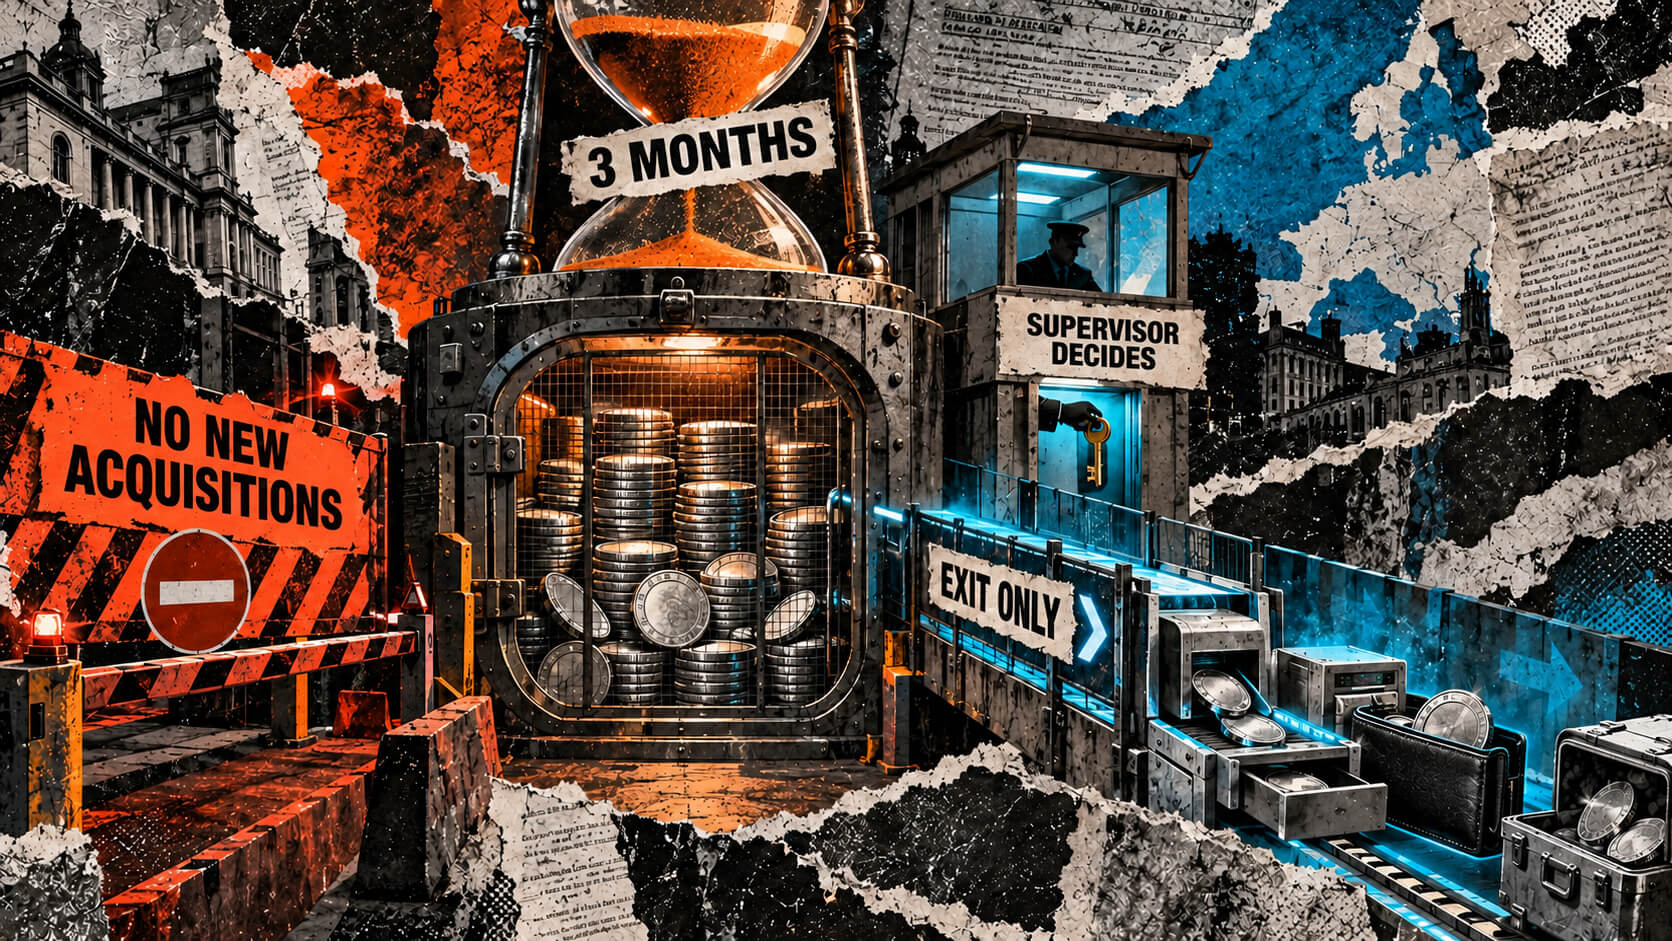
Crypto firms authorized under the EU's Markets in Crypto-Assets regulation (MiCA) should resolve EU clients' remaining exposure to non-compliant stablecoins through their services within three months, according to a new opinion from the bloc's markets watchdog.
The European Securities and Markets Authority (ESMA) published the opinion Oct. 8. Where national regulators find legacy exposures, ESMA said they should require remediation as soon as possible and no later than three months after publication, or about Jan. 8, 2027.
National regulators may allow firms that do not yet comply to provide strictly limited services needed for an orderly wind-down and to avoid harm to clients. These can include liquidation, conversion, withdrawal, transfer or safekeeping of existing holdings.
Those exit services should be time-limited, clearly communicated to clients and closely supervised. They should not enable new acquisitions, promotion, active distribution or continued market availability.
National supervisors decide whether to allow them, so customers do not automatically get three months of continued service.
The opinion's legal route is Article 66(1) of MiCA, which requires providers to act in clients' best interests. In ESMA's view, providing any MiCA service involving a non-compliant stablecoin should give rise to a presumption that it is incompatible with that duty, whether or not the individual service constitutes an offer to the public or admission to trading.
ESMA argued that providers cannot adequately mitigate the risks created by missing issuer-level safeguards. Warnings, disclosures and client acknowledgments would not resolve those concerns.
ESMA's Jan. 17, 2025 statement left mere custody and transfers open while restricting trading and other services that constituted public offers. The new opinion complements that guidance, preserving the earlier offer-to-the-public interpretation while adding expectations under providers' existing duties.
In its Sept. 30 MiCA-review response, ESMA had sought legislation prohibiting all licensable services involving non-compliant stablecoins, without specifying an implementation date or wind-down path for that proposal.
The October opinion adds a timetable and supervised exit arrangements under current MiCA obligations to the legislative request from Oct. 3.
Access to stablecoins beyond trading
ESMA's opinion names no token or issuer. However, Tether's USDT is among the assets Coinbase's EEA retail guidance labels MiCA-non-compliant.
Kraken's guidance, updated April 13, lists USDT among stablecoins delisted for EEA trading while still permitting deposits and withdrawals, although it discourages deposits.
Removing USDT trading pairs alone may not satisfy ESMA's expectations where a MiCA-authorized provider continues servicing it as a non-compliant token. Remaining services would need to fit any narrowly permitted, supervised wind-down.
For existing holders, the practical question is which exit services their provider and national supervisor allow. The opinion concerns access through regulated EU firms, but it does not impose a worldwide ban on owning USDT.
The post EU regulators target non-compliant stablecoins with a 90-day deadline appeared first on CryptoSlate.